Future Services: CRA Conformity Assessments
Cyber Resilience Act
Consult our experts. We are happy to support you.
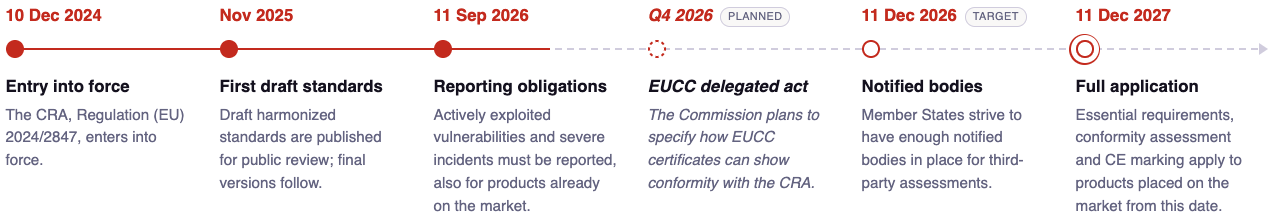
The Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, establishes cybersecurity requirements for products with digital elements placed on the EU market. It aims to protect consumers and businesses by requiring manufacturers of products within its scope to address cybersecurity during design and development, and to handle vulnerabilities throughout the support period. Depending on the product classification and applicable conformity assessment path, independent assessment by a notified body may be required. Module B provides EU-type examination of the product’s technical design and development, and the manufacturer’s vulnerability handling processes.
What atsec offers:
atsec Sweden operates a notified conformity assessment body, accredited (note: accreditation and notification currently ongoing) by SWEDAC, Sweden’s national accreditation body, against requirements specified in the ISO/IEC 17065 standard. Our notified body offers product certification according to Module B.
Module B + C
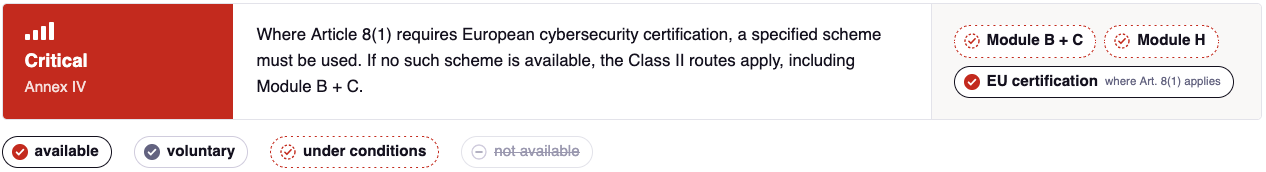
Module B is an EU-type examination by a notified body. Under the CRA it is followed by Module C, through which the manufacturer ensures conformity to EU-type based on internal production control. Whether B + C is available or needed depends on the product category and applicable assessment rules. Note that module B alone does not constitute a CRA conformity assessment procedure.
Why our services are important to you:
Our Notified Body services provide an independent assessment of your product’s design and vulnerability handling processes, with clear findings to help you address compliance gaps. Where your conformity assessment route requires third-party involvement, our Module B assessment supports the certification needed to bring your product to the EU market.
Product categories and conformity assessment:



EUCC and the Presumption of Conformity
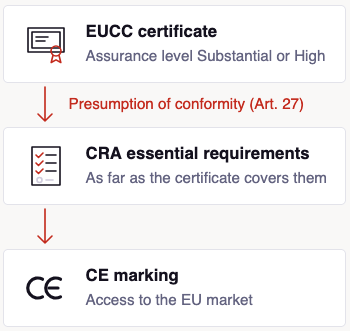
Under Article 27 of the CRA, a European cybersecurity certificate can give a presumption of conformity with the CRA’s essential requirements, as far as the certificate covers them. The Commission is preparing a delegated act that specifies how EUCC certificates can be used for this.
atsec ITSEF evaluates and atsec CB certifies products under EUCC today. Talk to us about how an EUCC certificate can support your CRA conformity.
Still have questions?
Can’t find what you’re looking for? Let’s talk!
Common Criteria Evaluation
The Common Criteria (CC), also known as ISO 15408, is an internationally recognized standard used to specify and assess the security of IT products.
Common Criteria Product Certification
atsec CB, accredited by SWEDAC, certifies products under the European Cybersecurity Certification Scheme (EUCC) at assurance levels Substantial and High.
Security Evaluation Standard for IoT Platforms (SESIP)
SESIP provides a common methodology for evaluating the security of connected products and the platforms they are built on.
The Information Security Provider
Read Our Latest Blog Articles
Learn the latest and greatest about information security. You’ll find insights and analyses of recent developments in technology and policy on our blog.
-
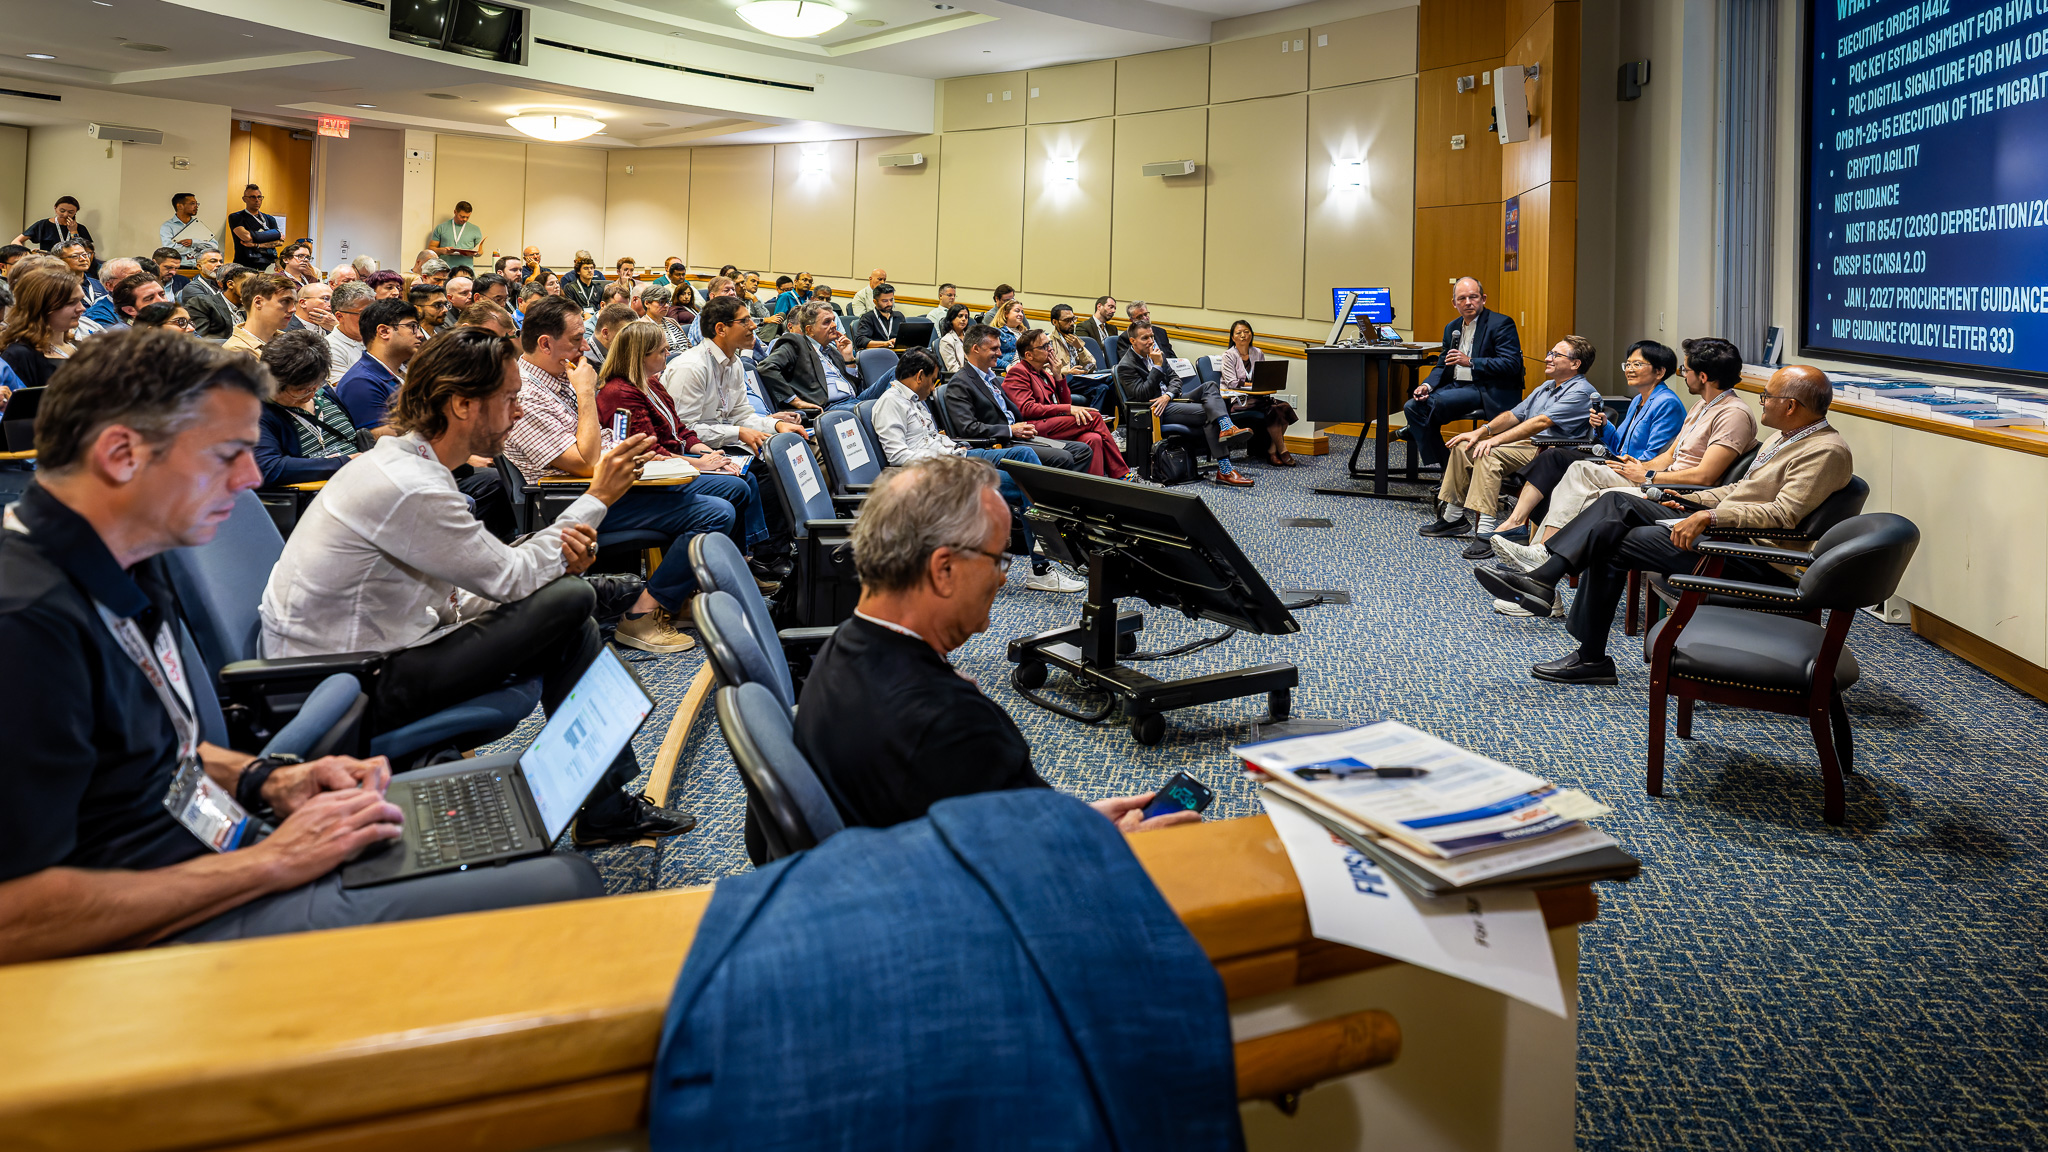
Making the Future Accessible at FIPS ‘n’ Chips 2026
FIPS ‘n’ Chips was a huge success, and part of its magic was its accessibility.
-
From the Forum to the Future: atsec Sponsors the 30th CCUF Workshop in Rome
On September 25, 2026, the Common Criteria community gathered in Rome for the second day of the 30th CCUF Workshop.